Security Engineer
Hire a security engineer for incident response and hardening
When a production server is owned, the clock matters more than the credential. I do the full incident response workflow — evidence-preserving triage, eradication, credential rotation, patching (including hand-written patches when the vendor fix has not shipped), and hardening that makes round two expensive.
The part most people get wrong
The instinct when a server is compromised is to reboot it. That destroys the volatile evidence — running processes, open connections, mapped memory — that tells you what the attacker took and how they got in. The first two hours decide whether you learn anything.
What you get
- →Evidence-preserving triage: full process tree, network connections, auth logs, crontabs, SSH trust audit and a raw disk image before anything is killed.
- →Eradication of cryptominers, reverse shells, persistence crontabs, unauthorized SSH keys and modified rc.local.
- →Custom CVE patches when the vendor fix is pending — CVE-2024-45519 was closed on a live Zimbra server with a hand-written 40-line Perl patch, same-day, 12 minutes of downtime.
- →Full credential rotation on the assumption the attacker already has everything.
- →fail2ban + firewalld + SSH key-only auth + root login disabled + auditd rules on sensitive paths.
- →Application-layer hardening: AES-256-GCM at rest, JWT refresh-token rotation, RBAC, TOTP 2FA, audit logging.
- →Authorized penetration testing with an agreed written scope and a findings report ranked by exploitability.
- →A written incident report with timeline, actions and residual risks — the document your insurer and counsel will ask for.
Proof — shipped and in production
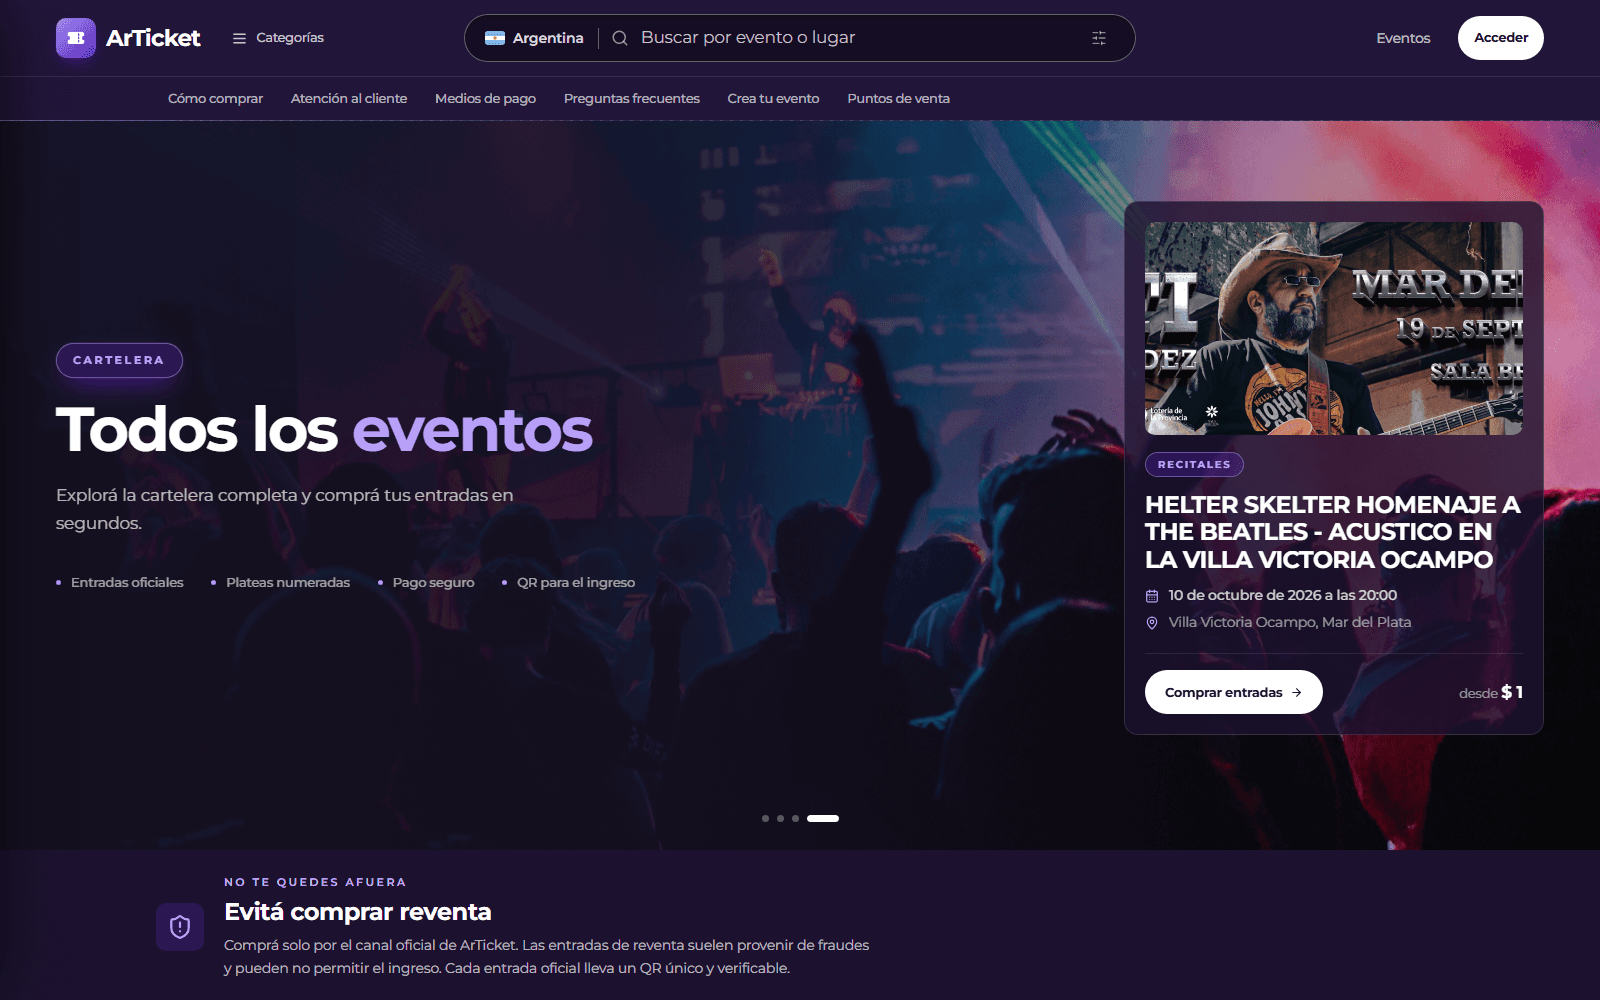
ArTicket Platform
A ticketing operator was renting its platform. The own 2D canvas seat-map engine runs at 39fps on 10k+ seats, and the operator owns it now.
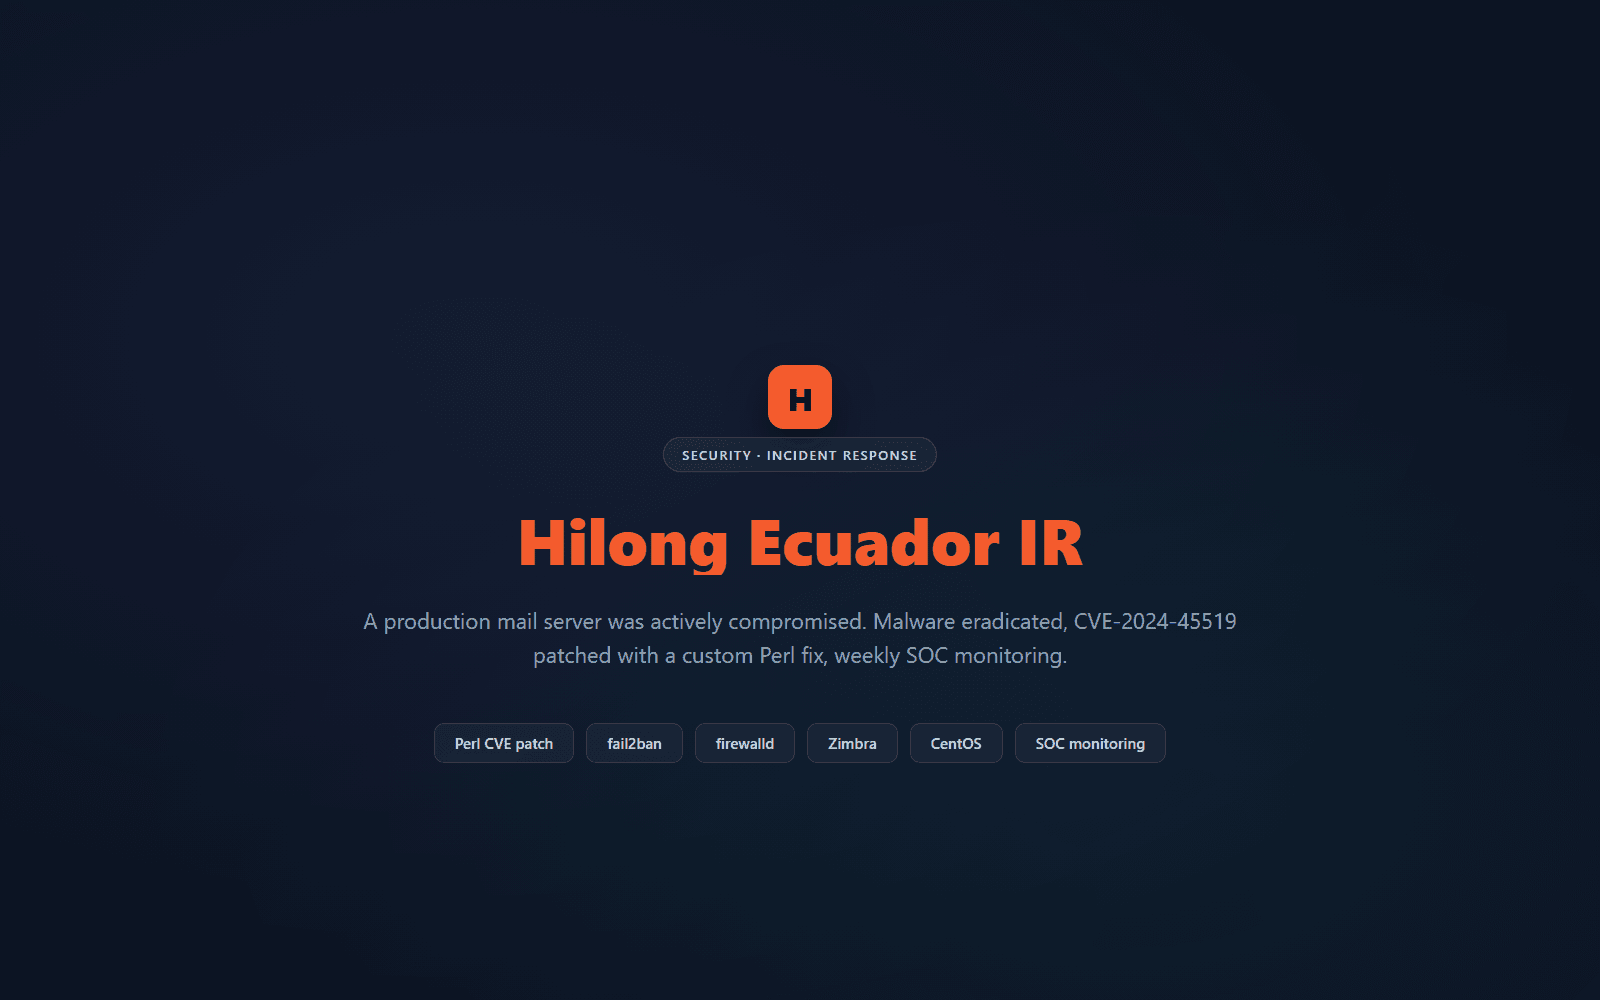
Hilong Ecuador Incident Response
A production mail server was actively compromised. Malware eradicated, CVE-2024-45519 patched with a custom Perl fix, and weekly SOC monitoring took over.
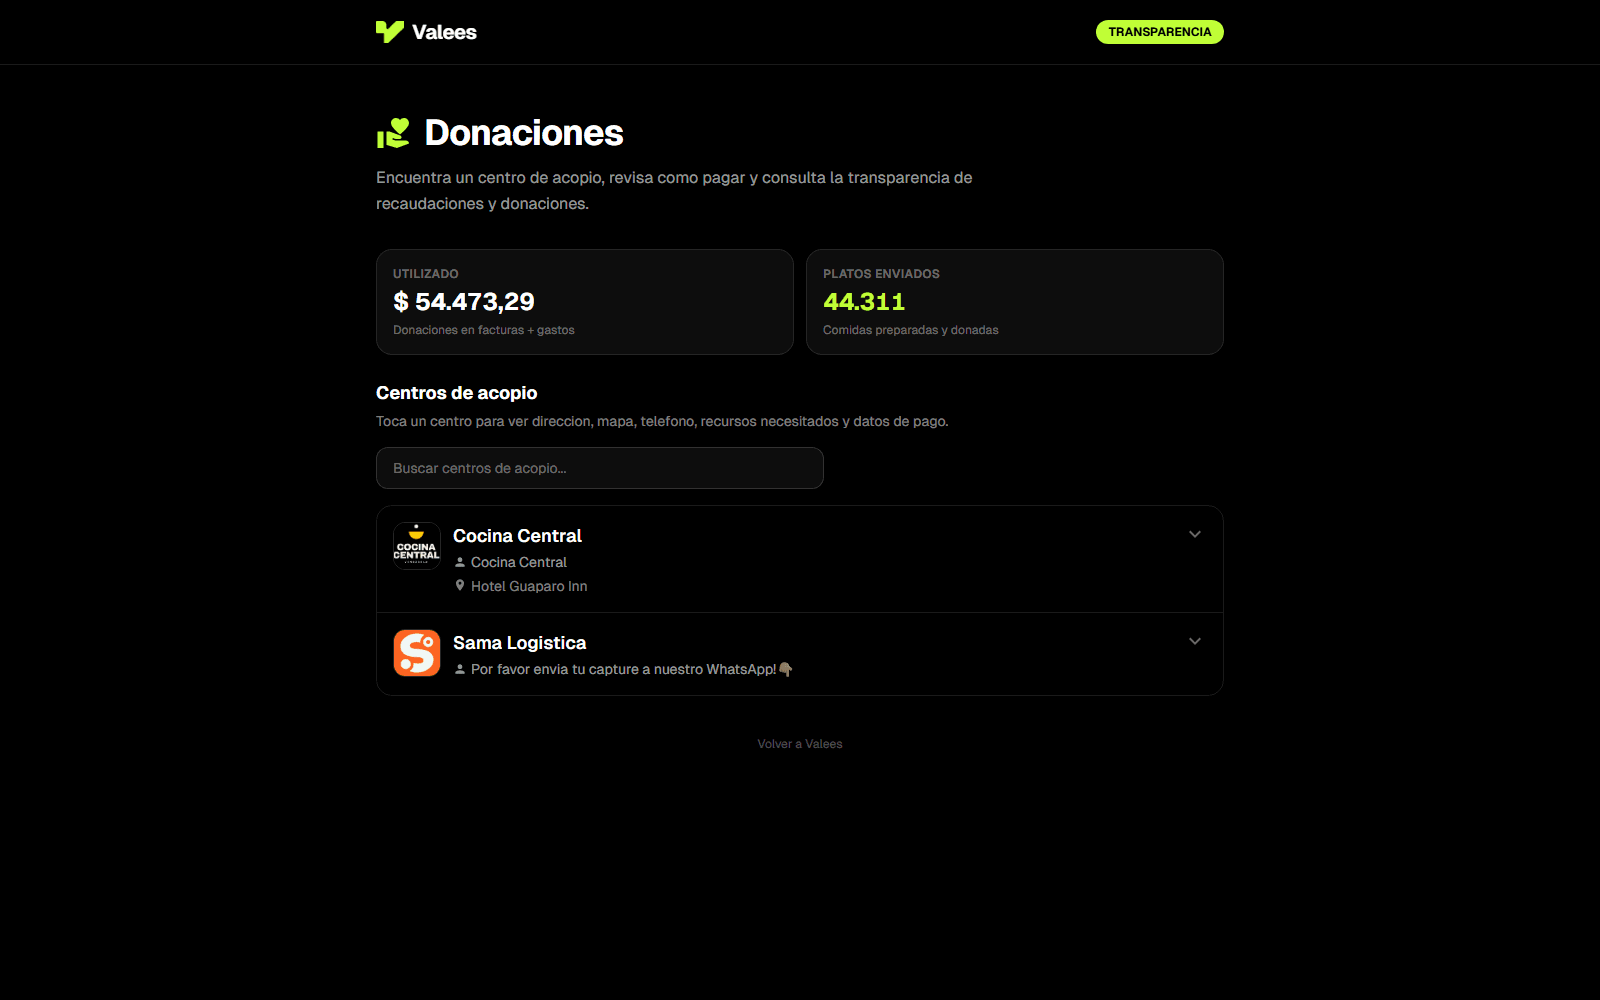
valee.app (Secure Mobile)
A mobile app needed to survive real attackers, not a checklist. Cryptography, pentesting and secure authentication baked into every layer, iOS and Android.
Frequently asked
Our server is compromised right now. What do we do first?+
Do not reboot it. Do not kill the suspicious process. Isolate it at the network switch level if you can — that stops the attacker from reacting while preserving the running state. Then send access. The first two hours are observation, because that is where the answers live.
Do you do offensive security work?+
Authorized penetration testing against systems whose owner signs a written scope, yes. Anything without that authorization, no — that is the line between security work and a crime, and it is not negotiable regardless of the budget.
Is a one-off cleanup enough?+
Rarely. A server that was owned once is a known-reachable target. The eradication is the emergency; the hardening plus weekly SOC review is what changes the odds. Most clients who go through an incident take the monitoring retainer afterward.
This role is also called
- cyber security expert
- cybersecurity consultant
- infosec engineer
- incident responder
- penetration tester
- security consultant
Start with a written brief
Describe what the business is losing today and what the target outcome looks like. I come back with a concrete plan against that document — in English, Spanish, Portuguese or Polish.
Other roles
Full-Stack Developer
One person who owns the whole thing — database schema, API, frontend, deployment, and the production incident at 2am. No handoffs between a backend contractor and a frontend contractor who blame each other when something breaks.
AI Engineer
Not a prompt consultant. An engineer who puts an LLM inside a process that already runs money through it — with cost routing, grounding, guardrails, escalation to humans, and a test suite that catches regressions before customers do.
Blockchain Developer
Contracts that shipped to mainnet and held real value — not a tutorial fork with the variable names changed. Vetra, a USD-backed stablecoin on Polygon with Chainlink Functions verifying reserves in real time, is the reference.
Business Automation Engineer
Not a Zapier consultant. An engineer who replaces the spreadsheet, the WhatsApp group and the clipboard with software the team stops having to think about — written in code you own, on infrastructure you control, with no per-execution billing.
Fintech Developer
The money layer, built with the paranoia it deserves. Signed webhooks, idempotent handlers, integer minor units, append-only ledgers, row-level locks. The boring rules that prevent the entire class of "the numbers do not add up" tickets.
WhatsApp API Developer
Official WhatsApp Business Cloud API via a Meta-approved BSP. Not Baileys, not Evolution, not a QR-scanning wrapper that gets the client's number banned in a week. The integration that survives contact with a real business.
Industrial Automation & IoT Engineer
Sensors are cheap now. The expensive part is turning a telemetry firehose into an alert that reaches the right person before the damage is done — and not one alert per reading, which trains everyone to ignore them.
Booking System Developer
The booking engine your business actually runs on — owned outright, not rented per seat. Real-time calendar sync, WhatsApp reminders in your voice, payments into your own account, and a cancellation queue that refills the slot before the front desk even notices.